Shieldworkz Featured in Elektroniknet
Boston Scientific Cyber Incident: Timeline, Impact and Analysis
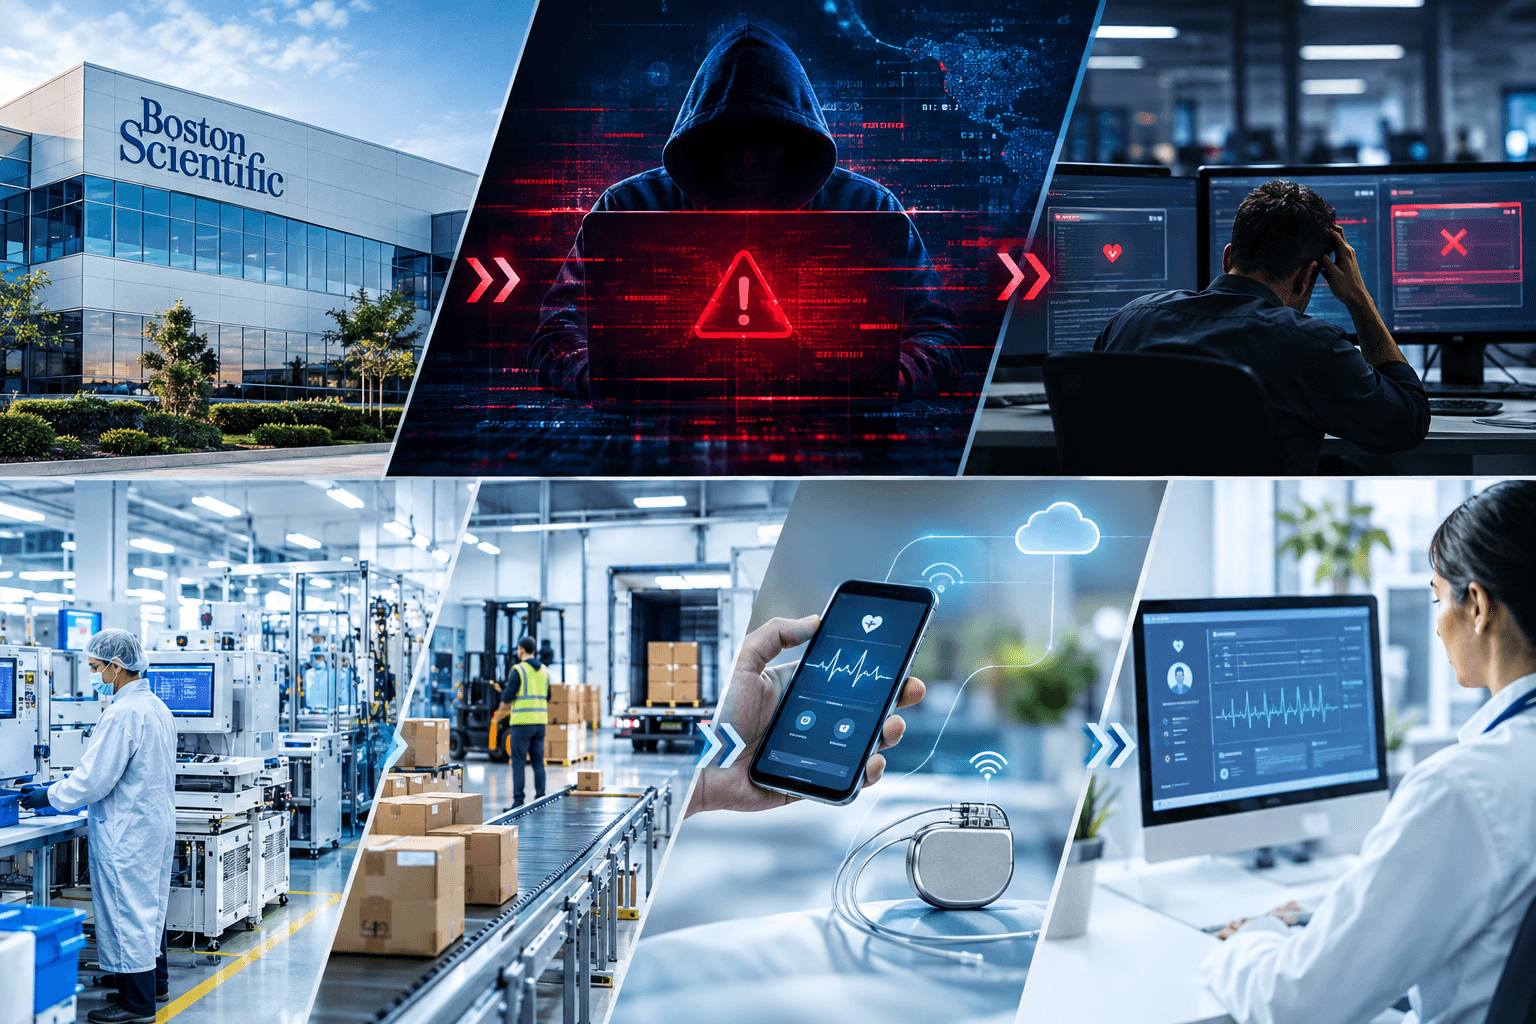
Boston Scientific identified the incident on August 25, 2026, and disclosed it to the SEC the following day, citing disruption to its IT network and key business applications, including order processing and shipping. On September 9, the company reported that manufacturing, order fulfillment and shipping were fully restored, and that remote monitoring activation for cardiac devices had resumed.
The coverage behind this page included Shieldworkz analysis of the incident. It was based on publicly available information and is interpretation, not a forensic finding. The company has not publicly confirmed the initial attack vector or the party responsible.

Boston Scientific Cyber Incident: Timeline, Impact and Analysis
Boston Scientific identified the incident on August 25, 2026, and disclosed it to the SEC the following day, citing disruption to its IT network and key business applications, including order processing and shipping. On September 9, the company reported that manufacturing, order fulfillment and shipping were fully restored, and that remote monitoring activation for cardiac devices had resumed.
The coverage behind this page included Shieldworkz analysis of the incident. It was based on publicly available information and is interpretation, not a forensic finding. The company has not publicly confirmed the initial attack vector or the party responsible.

Why This Coverage Matters
Industrial and connected-product organizations rarely run on isolated systems. Enterprise IT supports ERP, which schedules production and releases shipments. Identity platforms grant access across office, plant and cloud environments. Remote access supports engineering and maintenance, and cloud services support connected products.
When these layers are secured as separate domains, the dependencies between them go unmanaged. Controllers and production equipment may be untouched while the systems that authorize, schedule and ship their output are unavailable.
That is why the traditional split between IT security and operational security becomes inadequate. The more useful question is which business processes cross that boundary, and what happens to them when one side is lost.
Why This Coverage Matters
Industrial and connected-product organizations rarely run on isolated systems. Enterprise IT supports ERP, which schedules production and releases shipments. Identity platforms grant access across office, plant and cloud environments. Remote access supports engineering and maintenance, and cloud services support connected products.
When these layers are secured as separate domains, the dependencies between them go unmanaged. Controllers and production equipment may be untouched while the systems that authorize, schedule and ship their output are unavailable.
That is why the traditional split between IT security and operational security becomes inadequate. The more useful question is which business processes cross that boundary, and what happens to them when one side is lost.
Shieldworkz Perspective
Shieldworkz did not investigate this incident. This is how we approach the problem it describes.
Start with dependencies. Map which digital and business services production continuity actually needs, including ERP, identity, remote access and third-party connections, and treat them as part of the operational risk model. Understand privileged-access exposure, since one identity can span IT and plant systems.
Then limit how far a problem can travel. Separate critical environments where it makes sense, and monitor communications across IT/OT boundaries so unusual activity is visible early. Prepare isolation options that contain an issue without unnecessarily halting critical operations.
Finally, plan for recovery as an operational exercise. Maintain resilient recovery paths and test whether operations can continue, not just whether backups exist. Connected products, industrial systems and supporting infrastructure form one ecosystem.
Why This Recognition Matters
Public coverage of incidents like this shifts the discussion from "Was the device compromised?" to "What operational processes depend on the systems surrounding that device?" Cyber resilience has to consider the full chain, from digital infrastructure to operational process to customer or patient impact. Careful analysis helps teams ask it before an incident forces the issue.
Key Takeaways From the Coverage
A working physical product does not guarantee operational continuity; the surrounding systems decide whether it can be built, released and supported.
Enterprise IT dependencies, such as ERP and business applications, can become production dependencies.
Identity and access sit across environments, so their exposure has consequences beyond conventional IT.
Centralized systems need tested fallback and recovery procedures, not only backups.
Assessments should follow dependencies across the whole ecosystem, rather than stopping at asset vulnerabilities.
Shieldworkz Perspective
Shieldworkz did not investigate this incident. This is how we approach the problem it describes.
Start with dependencies. Map which digital and business services production continuity actually needs, including ERP, identity, remote access and third-party connections, and treat them as part of the operational risk model. Understand privileged-access exposure, since one identity can span IT and plant systems.
Then limit how far a problem can travel. Separate critical environments where it makes sense, and monitor communications across IT/OT boundaries so unusual activity is visible early. Prepare isolation options that contain an issue without unnecessarily halting critical operations.
Finally, plan for recovery as an operational exercise. Maintain resilient recovery paths and test whether operations can continue, not just whether backups exist. Connected products, industrial systems and supporting infrastructure form one ecosystem.
Why This Recognition Matters
Public coverage of incidents like this shifts the discussion from "Was the device compromised?" to "What operational processes depend on the systems surrounding that device?" Cyber resilience has to consider the full chain, from digital infrastructure to operational process to customer or patient impact. Careful analysis helps teams ask it before an incident forces the issue.
Key Takeaways From the Coverage
A working physical product does not guarantee operational continuity; the surrounding systems decide whether it can be built, released and supported.
Enterprise IT dependencies, such as ERP and business applications, can become production dependencies.
Identity and access sit across environments, so their exposure has consequences beyond conventional IT.
Centralized systems need tested fallback and recovery procedures, not only backups.
Assessments should follow dependencies across the whole ecosystem, rather than stopping at asset vulnerabilities.

About Shieldworkz
Shieldworkz helps organisations secure Operational Technology (OT), IoT and Cyber-Physical Systems (CPS) across industrial and national infrastructure. Our threat research team blends sector-aware telemetry, hunt-driven detection, and hands-on incident response to find hidden exposure and build resilient recovery paths.
About Shieldworkz
Shieldworkz helps organisations secure Operational Technology (OT), IoT and Cyber-Physical Systems (CPS) across industrial and national infrastructure. Our threat research team blends sector-aware telemetry, hunt-driven detection, and hands-on incident response to find hidden exposure and build resilient recovery paths.
Visit our website: https://shieldworkz.com
For press inquiries and expert interviews, contact: info@shieldworkz.com
Stay ahead of tomorrow’s threats with Shieldworkz, your partner in proactive OT cybersecurity.
Learn More & Resources
Visit our website: https://shieldworkz.com
For press inquiries and expert interviews, contact: info@shieldworkz.com
Stay ahead of tomorrow’s threats with Shieldworkz, your partner in proactive OT cybersecurity.
Learn More & Resources
Read the news article