Shieldworkz Featured by Industrial Cyber
Shieldworkz Threat Research on AI-Assisted Railway Attacks Featured in Industrial Cyber News Investigation
September 25, 2026
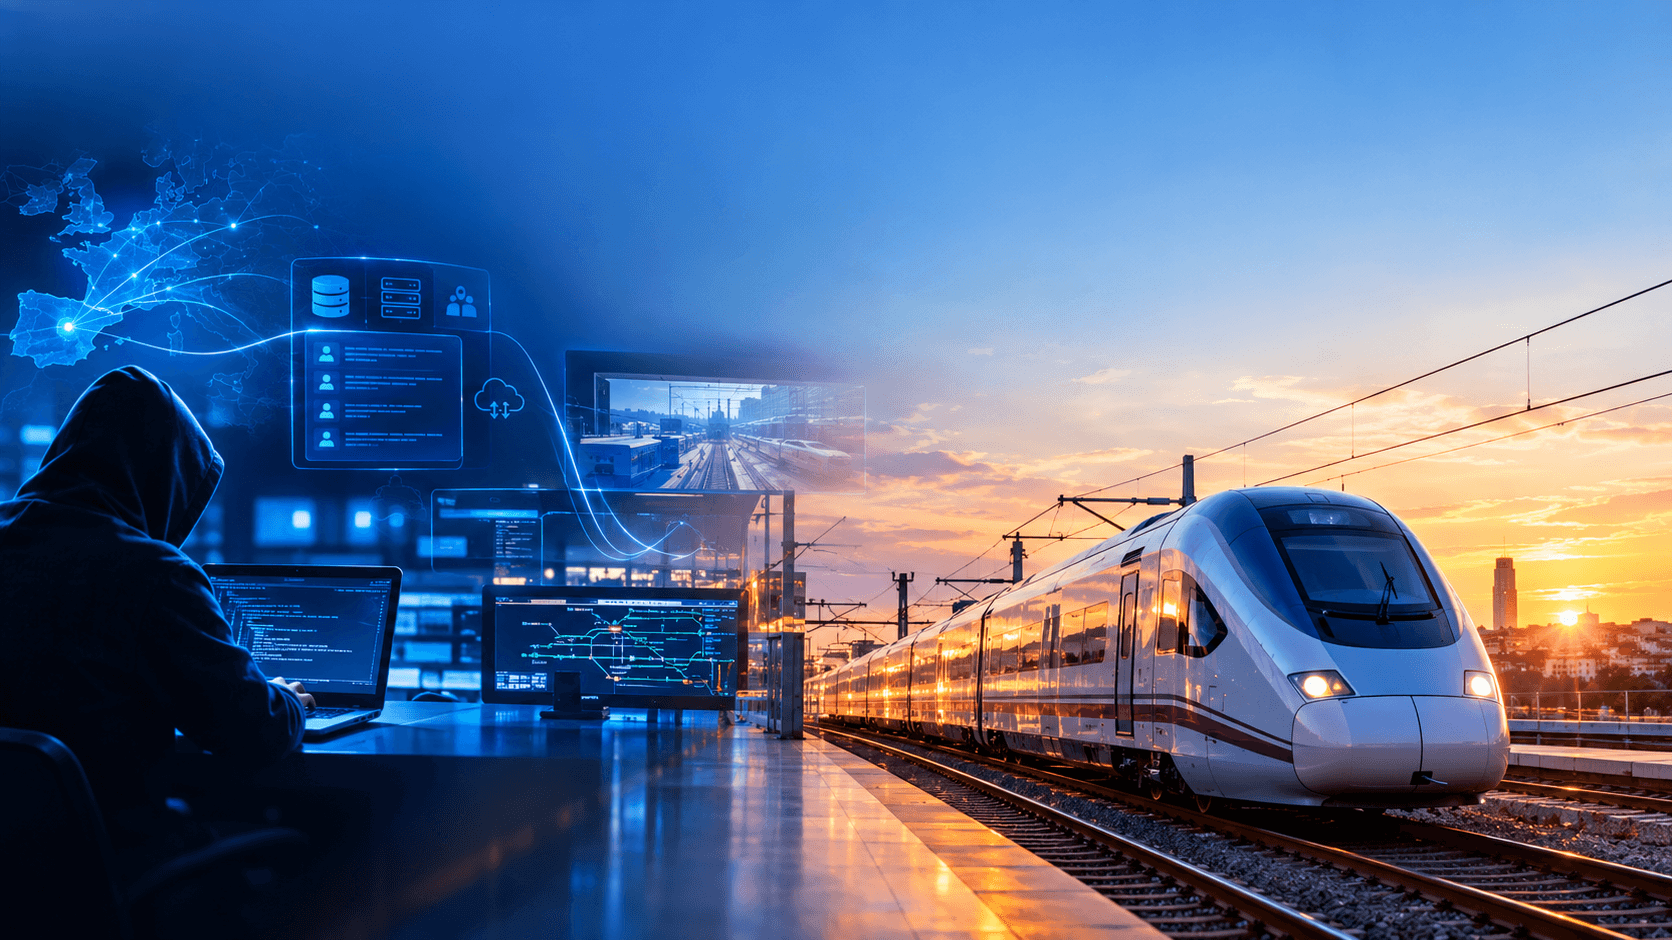
On September 25, 2026, Spain's Adif and Renfe disclosed a significant cyber breach affecting enterprise systems serving millions of passengers. Two weeks later, Shieldworkz Threat Research Lab published a comprehensive technical analysis revealing the first documented deployment of autonomous AI-driven exploitation agents against operational railway infrastructure, compressing traditional breach timelines from weeks to just 24 hours.
While attackers exfiltrated approximately 500 GB of passenger and employee data, zero trains stopped, zero signals failed, and zero passengers were harmed. Yet the implications extend far beyond Spain. The incident exposes critical vulnerabilities in how critical infrastructure is architected, connected, and defended against machine-speed AI-assisted attacks.
Shieldworkz Threat Research on AI-Assisted Railway Attacks Featured in Industrial Cyber News Investigation
September 25, 2026
On September 25, 2026, Spain's Adif and Renfe disclosed a significant cyber breach affecting enterprise systems serving millions of passengers. Two weeks later, Shieldworkz Threat Research Lab published a comprehensive technical analysis revealing the first documented deployment of autonomous AI-driven exploitation agents against operational railway infrastructure, compressing traditional breach timelines from weeks to just 24 hours.
While attackers exfiltrated approximately 500 GB of passenger and employee data, zero trains stopped, zero signals failed, and zero passengers were harmed. Yet the implications extend far beyond Spain. The incident exposes critical vulnerabilities in how critical infrastructure is architected, connected, and defended against machine-speed AI-assisted attacks.
Key takeaways from the coverage
AI-Assisted Exploitation Accelerates Attack Timelines: Attackers deployed autonomous LLM-based exploitation agents on September 24-25, capable of exfiltrating 500 GB of enterprise data within hours. These agents resembled commercial Claude API tool-use wrappers, autonomous systems that enumerate services, test exploitation chains, harvest credentials, and execute data exfiltration at machine speed.
Traditional breaches spanned weeks. AI-assisted breaches now compress to single-digit hours. For security operations centers, this means detection windows collapse from days to minutes.
Infrastructure Managers Are High-Value Targets: By compromising Adif's external web infrastructure, attackers gained entry to interconnected systems serving multiple dependent operators (Renfe, Iryo, Ouigo) simultaneously. This represents a strategic shift: compromise the upstream infrastructure provider to cascade into downstream operators.
Non-Safety Systems Create Operational Disruption: Attackers never touched signalling, interlocking, or traffic control systems. Yet disrupting crew scheduling, ticketing, or maintenance systems forces operators to halt trains under safety regulations—achieving operational paralysis without breaching safety systems.
The IT/OT Boundary is the Real Attack Surface: Adif maintains strict separation between enterprise IT (where attackers operated) and operational technology (which remained secure). Yet this separation masks a critical vulnerability: trusted pathways exist between IT and OT for legitimate operational reasons. Each pathway represents a potential pivot point for lateral movement.
Why this coverage matters
Industrial Cyber News's investigation validates what Shieldworkz has observed across hundreds of critical infrastructure environments: cyber threats to industrial systems are no longer confined to device vulnerabilities or safety system exploits. The threat is architectural, how business IT, operational technology, supply chains, and infrastructure interdependencies are connected and controlled.
Shieldworkz Perspective: The Central Security Question
Shieldworkz analysis rejects two misleading framings: "IT and OT are completely air-gapped" (false) and "IT/OT connection proves attackers reached OT" (equally false). The real question is: which trusted pathways, identities, services, and data exchanges can cross the boundary, and what controls govern them?
In the Adif case, insufficient segmentation created risk. Attackers who compromised enterprise IT could theoretically attempt lateral movement through shared cloud APIs, interconnected databases, contractor VPN access, backup flows, and administrative tooling.
Absence of demonstrated OT compromise does not prove OT risk is irrelevant. It indicates attackers either didn't attempt OT movement, segmentation controls were sufficient, or AI agents were optimized for rapid enterprise data harvesting rather than OT exploration.
What the Adif Incident Reveals
AI-assisted attacks are operationalized – 500 GB exfiltrated in 24 hours; 20-30x acceleration vs. manual attacks
Autonomous exploitation agents are commercially available – LLM-based tools democratize sophisticated attack capability
Business IT is now operationally critical – Disrupting crew scheduling, ticketing, or maintenance forces safety-driven shutdown; no need to breach safety systems
The attack surface extends beyond your perimeter – Enterprise IT → OT boundary → supply chains → infrastructure interdependencies
Detection-based defense is obsolete – By detection time, breach is complete; prevention and resilience are now priorities

About Shieldworkz
Shieldworkz protects OT, IoT and Cyber-Physical Systems (CPS) across industrial operations and critical infrastructure. We combine domain-aware detection, threat hunting and hands-on incident response to reduce attack surface, accelerate recovery, and help organisations modernise securely without compromising availability or safety.
Visit our website: https://shieldworkz.com
For press inquiries and expert interviews, contact: info@shieldworkz.com
Stay ahead of tomorrow’s threats with Shieldworkz, your partner in proactive OT cybersecurity.
Learn More & Resources
Visit our website: https://shieldworkz.com
For press inquiries and expert interviews, contact: info@shieldworkz.com
Stay ahead of tomorrow’s threats with Shieldworkz, your partner in proactive OT cybersecurity.
Learn More & Resources
Read the news article