Team Shieldworkz
On May 7, 2021, a compromised VPN password helped bring a pipeline to a standstill. That pipeline carried roughly 45 percent of the fuel used on the U.S. East Coast. The attackers never touched the controllers that run its pumps and valves. The company shut down operations anyway, for about six days, because it could not quickly prove that the control network was clean.
That decision, made without full visibility, is the real lesson of the Colonial Pipeline incident. Most operators have invested in firewalls, monitoring tools, and policies. Far fewer can answer three plain questions on short notice: What do we own? How is it connected? And which weaknesses could actually stop production or endanger people?
IEC 62443 gives industrial organizations a disciplined way to answer those questions. It is the most widely adopted international standard series for securing industrial automation and control systems. But the standard only helps if the assessment behind it is thorough, repeatable, and defensible. For many teams, that is where the struggle begins. Spreadsheets, scattered documents, interviews, and a few overstretched engineers cannot keep pace with a portfolio of plants.
This Blog explains what a modern IEC 62443 risk assessment platform should deliver, which real incidents show why the quality of an assessment matters, how to evaluate the options, and where OThello Assess from Shieldworkz fits. If you lead OT security, run a plant, or answer to a board about operational risk, you will leave with a clear framework for making a confident decision.
Why OT security leaders should read this: an assessment is not a report you file away. It is the evidence base for budget requests, insurance conversations, regulator questions, and every decision about which risk to reduce first. A weak assessment process quietly weakens all of them.
Why IEC 62443 Has Become the Reference Standard for Industrial Security
Industrial environments are not office networks. A controller that has run reliably for fifteen years cannot be rebooted on a Tuesday afternoon for a patch. A safety system must behave predictably above all else. A historian, a robot cell, and a substation relay all speak different languages and carry different consequences when they fail.
IEC 62443 was written with those realities in mind. Developed jointly by the International Society of Automation and the International Electrotechnical Commission, it treats security as a shared responsibility among asset owners, system integrators, and product suppliers. It also ties security effort to consequence, so a water pump station and a pharmaceutical line are not forced into the same answer.
Regulators, insurers, and customers increasingly point to the standard when they ask how an industrial operator manages cyber risk. That makes a clean, evidence-backed assessment more valuable every year.

What the IEC 62443 Series Covers
The series is organized into groups, and each part speaks to a different audience. Understanding the structure helps you see which parts an assessment platform must handle well.
Part | Focus | Who it matters most to |
62443-1-1 | Terminology, concepts, and reference models | Everyone; sets the shared vocabulary |
62443-2-1 | Requirements for an industrial security management program | Asset owners and plant leadership |
62443-2-4 | Security capabilities of service providers | Integrators and maintenance partners |
62443-3-2 | Security risk assessment and system design | Asset owners and system designers |
62443-3-3 | System security requirements and security levels | System designers and engineers |
62443-4-1 | Secure product development lifecycle | Product suppliers |
62443-4-2 | Technical security requirements for components | Product suppliers and system designers |
Table 1: How the IEC 62443 series is organized
Part 3-2 is the one that matters most for risk assessment. It describes how to define the system under consideration, perform an initial risk assessment, divide the system into zones and conduits, run a detailed risk assessment for each, and document the outcome in a cybersecurity requirements specification. Everything else in the standard builds on that foundation.
Zones, Conduits, and Security Levels in Plain Terms
Two ideas sit at the center of the standard, and both are simpler than they sound.
Zones are groups of assets that share the same security needs, such as the safety systems for a process unit or the operator stations in a control room.
Conduits are the controlled communication paths between zones. Every route in or out of a zone is a conduit, and each one must be understood, restricted, and monitored.

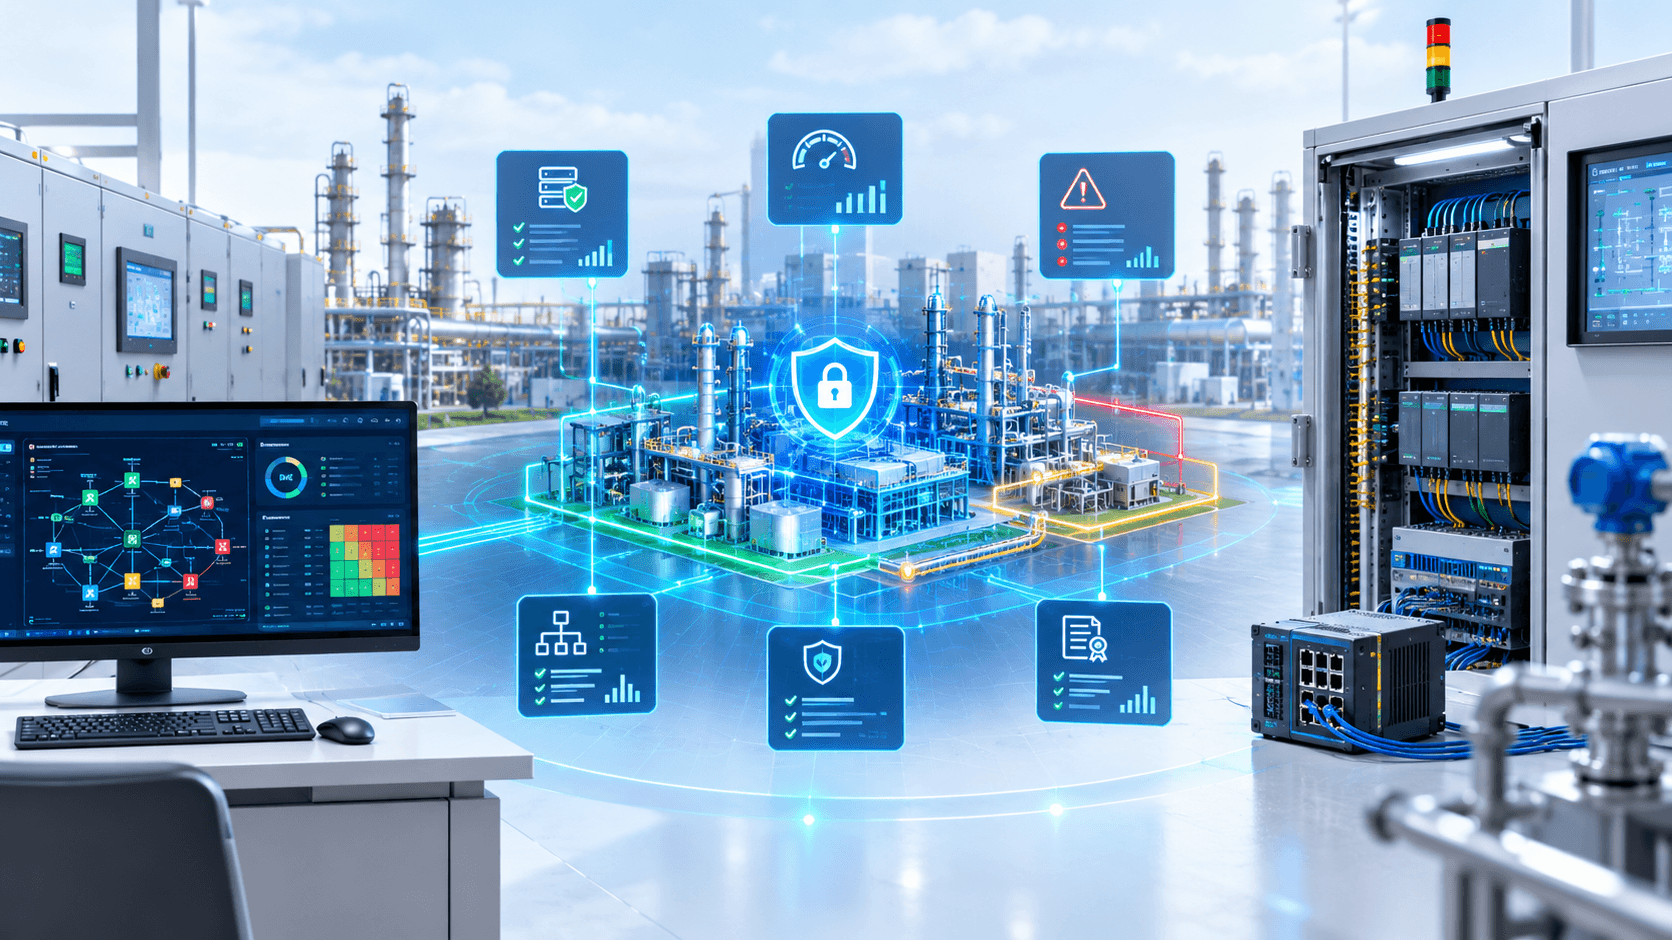
Figure 1: An example of how an industrial site can be divided into zones, with conduits controlling the paths between them. Target security levels vary by consequence.
Each zone is assigned a target security level based on how serious the consequences of a compromise would be and how capable a likely attacker is. The standard defines four levels.
Level | Protects against | Typical thinking |
SL 1 | Casual or accidental violations | Mistakes, unintended changes, basic exposure |
SL 2 | Intentional violations using simple means, low resources, and generic skills | Opportunistic attackers and commodity tools |
SL 3 | Intentional violations using sophisticated means, moderate resources, and industrial-specific skills | Skilled, motivated criminal or targeted groups |
SL 4 | Intentional violations using sophisticated means, extended resources, and industrial-specific skills with high motivation | Well-resourced adversaries; reserved for the highest consequence |
Table 2: IEC 62443 security levels
A good assessment goes one step further and distinguishes three numbers for every zone: the target level the zone needs, the capability level the installed products can support, and the achieved level actually in place today. The gaps between those numbers are your remediation roadmap. Calculating and tracking them by hand across dozens of zones is where manual processes start to crack.
Real Incidents That Show Why Assessment Quality Matters
Industrial attacks are rarely exotic. They usually succeed by exploiting something that was knowable in advance: an open remote path, a shared password, a network with no internal boundaries. The incidents below span a decade, and the same themes keep returning.
Year | Incident | What happened | Assessment lesson |
2015 | Ukrainian power distribution | Attackers took remote control of operator workstations at three regional utilities and opened breakers, leaving roughly 225,000 customers without power for hours. | Remote access and weak separation between business and control networks were the entry points. |
2016 | Kyiv transmission substation | Purpose-built malware spoke native substation protocols and interrupted power for about an hour. | Attackers had learned industrial protocols. Generic IT controls were not enough. |
2017 | Petrochemical safety system, Middle East | Attackers reached safety controllers and a plant shut down unexpectedly after the intrusion tripped the safety logic. | Safety systems need their own zone, strict conduits, and verified isolation. |
2019 | Global aluminum producer | Ransomware hit operations across dozens of countries and roughly 35,000 employees; production teams reverted to manual processes. | Resilience and recovery planning belong inside the risk assessment, not beside it. |
2021 | Florida water treatment facility | An intruder used remote access software to raise a chemical setting to a dangerous level. A vigilant operator noticed and reversed it. | Shared credentials and unmonitored remote tools turn a single login into a safety event. |
2021 | U.S. fuel pipeline | A compromised remote password led to a precautionary shutdown of pipeline operations for about six days. | Without clear visibility into network boundaries, organizations may shut down what they cannot verify. |
Table 3: Selected industrial incidents and what they teach
The Pattern Behind the Headlines
Read the table again and look for what is missing. None of these stories turns on an unknown flaw that nobody could have anticipated. Each turns on a path, a credential, or a boundary that a disciplined assessment would have flagged and ranked.
In Ukraine, the question was how a business network could reach operator stations. In Florida, it was who could log in remotely and from where. At the pipeline, it was whether the organization could demonstrate the separation between its commercial and operational systems. These are exactly the questions IEC 62443 asks.
The harder truth is that many organizations did have an assessment. What they lacked was one that was current, complete, and specific enough to drive action. That is a process problem, and process problems can be solved.
Risks and Challenges: Why Manual IEC 62443 Assessments Break Down
Teams rarely fail at assessments because they do not care. They fail because the work is heavy, the evidence is scattered, and the people who understand the plant are also the people running it. Five challenges come up again and again.
1. Evidence Lives Everywhere and Nowhere
To judge whether a control exists, an assessor needs network diagrams, firewall rules, asset lists, patch records, access policies, vendor contracts, and incident procedures. In a typical plant these sit in different formats, different systems, and different people's inboxes. Collecting, reading, and cross-checking them can consume more time than the analysis itself.
2. Asset Visibility Is Incomplete
You cannot assign a security level to a system you do not know exists. Many sites carry controllers installed decades ago, laptops that vendors left behind, and wireless links added during a shutdown and never documented. Asset lists drawn from memory or an old spreadsheet leave blind spots exactly where attackers look.
3. Zone Design Depends on Individual Judgment
Dividing a plant into zones and conduits is part science, part craft. Two assessors looking at the same site can draw different boundaries and reach different conclusions. Across a multi-site portfolio, that inconsistency makes it nearly impossible to compare sites fairly or to explain to leadership why one plant ranks above another.
4. Findings Are Not Ranked by Real Consequence
A long list of gaps is not a plan. Without a way to weigh each gap against operational and safety consequence, teams either try to fix everything or fix whatever is easiest. Budgets get spent on the visible while the dangerous quietly waits.

Figure 2: Prioritization should combine likelihood with operational and safety consequence. The placements shown are illustrative.
5. Audit and Reporting Pressure Keeps Growing
Customers, insurers, and regulators now ask for proof, not promises. Producing that proof by hand means reformatting the same findings for each request, and every reformat is a chance for errors or outdated numbers to slip through. When an auditor asks where a statement came from, the team needs to point to the underlying evidence within minutes.
Manual Effort Versus a Platform-Assisted Approach
Assessment task | Typical manual approach | Platform-assisted approach |
Evidence gathering | Email requests, shared folders, repeated follow-ups | Central intake with automated reading and tagging of documents |
Asset identification | Spreadsheets compiled from interviews and old diagrams | Assets extracted from evidence and flagged where data is missing |
Zone and conduit mapping | Hand-drawn diagrams, varying by assessor | Consistent proposals that engineers review and refine |
Control evaluation | Checklists scored by individual judgment | Requirement-by-requirement evaluation linked to source evidence |
Gap prioritization | Long lists ranked by instinct | Gaps ranked by consequence and exposure with transparent logic |
Multi-site consistency | Different formats and scoring at every site | One method and one scoring model across the portfolio |
Reporting and audit | Documents rebuilt for every request | Audit-ready reports generated from the same evidence base |
Reassessment | Starts almost from scratch | Builds on prior results and highlights what changed |
Table 4: Where a platform changes the work
What a Modern IEC 62443 Risk Assessment Platform Should Deliver
Not every tool that calls itself an assessment platform earns the label. A dashboard that scores a questionnaire is not the same as a system that reads your evidence, understands your plant structure, and produces conclusions an auditor will accept. When you evaluate options, look for seven capabilities. Each one removes a specific kind of manual burden.

Figure 3: The assessment workflow a platform should support end to end.
Automated Evidence Analysis
The platform should accept the documents you already have, such as architecture diagrams, policies, configuration exports, and procedures, and extract the facts that matter. The best implementations also show exactly where each conclusion came from, so an engineer can verify it in seconds. Automation without traceability simply moves the doubt somewhere else.
Asset Identification
A strong platform builds a working asset picture from the evidence provided and highlights what is unknown. A list of controllers, servers, network devices, and remote paths is useful. A list that clearly marks where information is missing is far more valuable, because it tells you what to go and find.
Security Zone and Conduit Mapping
Zone design is where assessments become consistent or fall apart. Look for a platform that proposes zones and conduits using clear logic, then lets your engineers adjust them. The goal is not to replace plant knowledge. It is to give every site the same starting structure so reviews focus on judgment, not formatting.
Control Evaluation Against Requirements
The platform should evaluate your environment against the relevant IEC 62443 requirements, including the seven foundational requirements: identification and authentication control, use control, system integrity, data confidentiality, restricted data flow, timely response to events, and resource availability. Results should show what is met, what is partly met, and what is missing, each with the supporting evidence.
Gap Prioritization
This is where a platform earns its keep. It should rank gaps using operational consequence, exposure, and the distance between target and achieved security levels. Leaders need to see why a gap sits at the top, and the logic should be transparent enough to defend in front of a board or a plant manager who disagrees.
Framework Mapping
Most industrial organizations answer to more than one set of expectations. A single finding may relate to IEC 62443 requirements, national guidance, sector rules, and internal policy. A platform that maps each finding across these frameworks lets you do the work once and answer many questions, rather than running parallel assessments that drift apart.
Audit-Ready Reporting
Reports should be ready for three audiences: executives who need a clear risk story, engineers who need specific actions, and auditors who need traceable evidence. If your team still spends days assembling a report after the analysis is done, the platform has not finished its job.
Where OThello Assess Fits in This Category
OThello Assess from Shieldworkz was built around the capabilities described above. It uses an AI-assisted workflow to read assessment evidence, identify assets, propose security zones, evaluate controls, prioritize gaps, map findings to frameworks, and produce audit-ready reports. The aim is simple: cut the manual overhead that slows assessments down, while keeping industrial security experts firmly in charge of the conclusions.
That last point matters. AI should accelerate the reading, structuring, and cross-checking. It should not be asked to understand a specific plant's process hazards or negotiate trade-offs between safety and availability. Those judgments belong to people who know the site. A platform built on that principle gives experts more time for decisions and less time for document handling.
OThello Assess is a particularly strong fit for organizations that need repeatable IEC 62443 assessments across multiple industrial sites. When every site follows the same method and the same scoring logic, leaders can compare plants, track progress over time, and direct investment where it will reduce the most risk.
Practical Recommendations: How to Run a Stronger IEC 62443 Assessment
Technology helps, but it works best inside a sound process. These practices consistently separate assessments that change outcomes from those that sit on a shelf.
Start with Consequences, Not Controls
Before looking at a single firewall rule, ask what the worst credible outcome would be at each process area. Loss of production, environmental release, equipment damage, and harm to people carry different weight. Target security levels should flow from those answers, not from a generic template.
Define the Scope Clearly
State exactly which systems, sites, and interfaces are inside the assessment. Include remote access, vendor connections, and engineering tools. Many serious findings hide in the connections that fall between teams.
Bring Engineers and Security Together Early
Operations staff know which changes are safe and which are not. Security staff know what attackers do. An assessment built by only one group is either unrealistic or unusable. Set aside review time with both in the room.
Assess in Waves, Not All at Once
For a large portfolio, begin with a pilot site, refine your method, then expand by risk and criticality. This avoids burning out your best people and builds an internal playbook other sites can follow.
Keep Evidence Alive
An assessment is only as current as its evidence. Set clear triggers for reassessment: a major network change, a new vendor connection, a significant incident, an acquisition, or a change in regulation. Platforms that retain prior results make these updates far lighter.
Link Every Finding to an Owner and a Decision
A finding without an owner is just an observation. Assign each priority gap to a named person, a target date, and a funding decision. Track closure in the same place you track the finding, so progress is visible to leadership.
A Practical 90-Day Starting Plan
Phase | Key activities | Outcome |
Days 1 to 30 | Confirm scope, gather existing evidence, select a pilot site, agree on target security levels | A clear starting baseline and shared understanding |
Days 31 to 60 | Run the pilot assessment, review zone and conduit proposals with engineers, evaluate controls | A defensible pilot report and refined method |
Days 61 to 90 | Prioritize gaps, assign owners, build the remediation roadmap, plan the next wave of sites | A funded plan and a repeatable process |
Table 5: A sample 90-day path to a repeatable assessment program
Questions to Ask Any Assessment Platform Vendor
Area | Question to ask | Why it matters |
Traceability | Can every conclusion be traced to a specific piece of evidence? | Auditors and engineers must be able to verify results |
Human oversight | Can our experts review and override automated results? | Plant knowledge must outrank automation |
Consistency | Does the same method apply to every site? | Enables fair comparison across the portfolio |
Prioritization | How is consequence factored into ranking? | Prevents effort going to low-risk fixes |
Frameworks | Can findings map to multiple frameworks automatically? | Avoids duplicate assessment work |
Data handling | Where does our sensitive plant data reside and who can see it? | Plant data is itself a security asset |
Reporting | Can we produce executive, engineering, and audit views? | Different audiences need different detail |
Ongoing use | How does the platform support reassessment over time? | Risk changes; the assessment must keep up |
Table 6: Evaluation checklist for assessment platforms
Sector Perspectives: Where Assessment Priorities Differ
IEC 62443 applies across industries, but the emphasis shifts with the environment. Here is how the priorities tend to differ.
Sector | Common focus areas | Typical concern |
Energy and utilities | Substation and SCADA communications, remote operations, vendor access | Grid reliability and public safety |
Manufacturing | Flat plant networks, engineering workstations, robotic cells and PLCs | Downtime that stops lines and shipments |
Water and wastewater | Remote access to small, distributed sites, chemical dosing controls | Public health and limited security staffing |
Oil, gas, and chemicals | Safety instrumented systems, process hazards, third-party maintenance | Environmental release and harm to people |
Table 7: Typical assessment emphasis by sector
Notice how many of these concerns trace back to remote access, vendor connectivity, and weak separation between zones. That is why a platform that handles zones, conduits, and consequence-based ranking well is so central to a credible program.
The Business Case: What Leaders Gain from a Better Assessment Process
For executives, the value of a stronger assessment process is practical. It is not about collecting more documents. It is about making sharper decisions with less friction.
Faster time to a baseline. Teams spend less time hunting for documents and more time reviewing conclusions.
Defensible budgets. Spending requests tie directly to ranked, evidence-backed risk.
Fewer surprises at audit time. Reports stay consistent because they come from one source of truth.
Better supplier and integrator conversations. Clear requirements make it easier to hold partners to account.
A stronger story for insurers and customers. You can demonstrate a living, repeatable process rather than a one-off report.
Lower dependence on a few experts. Knowledge is captured in the process, not just in people's heads.
How Shieldworkz Supports Organizations
Shieldworkz focuses exclusively on the security of industrial and critical infrastructure environments. Our teams combine hands-on plant experience with deep security expertise, so recommendations hold up on the plant floor as well as in the boardroom. Depending on where you are in your journey, we can help in the following ways.
IEC 62443 risk assessments. Structured assessments covering assets, zones, conduits, security levels, and control gaps, delivered with clear, prioritized findings.
OThello Assess. An AI-assisted assessment platform that reduces manual effort, supports repeatable multi-site assessments, and produces audit-ready outputs, with experts reviewing every conclusion.
Zone and conduit design. Practical segmentation designs that reflect how your plant actually operates, not how a diagram says it should.
Roadmaps and remediation planning. Gap closure plans sequenced by consequence, cost, and operational feasibility, so improvements fit into real maintenance windows.
Remote access and third-party risk reviews. Focused evaluations of the pathways most often used in industrial incidents.
Program maturity support. Help aligning policies, roles, and processes with IEC 62443 program requirements for asset owners.
Incident readiness. Exercises and response planning built around operational continuity and safe recovery.
Training for engineers and leaders. Practical sessions that give operations and security teams a shared language.
We work alongside your engineers and plant teams. The goal is not a thicker report. It is a security program your people understand, trust, and can sustain.
Frequently Asked Questions
1.What is an IEC 62443 risk assessment?
It is a structured review of an industrial control environment that defines the system, identifies assets, divides it into zones and conduits, evaluates threats and consequences, and sets target security levels. The results guide which controls to implement and in what order.
2.How is it different from an IT security assessment?
Industrial assessments put safety and availability first. They account for long equipment lifecycles, specialized protocols, limited patching windows, and the physical consequences of failure. An IT-focused approach often misses these considerations.
3.How often should an assessment be repeated?
At a minimum, whenever something significant changes: network redesigns, new vendor access, major incidents, expansions, or regulatory shifts. Many organizations also schedule a regular review cycle so the picture never goes stale.
4.Can software replace experienced assessors?
No. Software can take on the reading, structuring, cross-referencing, and report generation that consume so much time. The judgment about process hazards, operational trade-offs, and acceptable risk should stay with experienced people.
5.Is a platform worth it for a single site?
It can be, particularly if you expect frequent reassessment or customer and regulator requests. The value grows quickly with the number of sites because consistency and reuse multiply.
Conclusion: Make Your Assessments Repeatable and Defensible
The incidents of the past decade teach a consistent lesson. Industrial attacks succeed through gaps that were knowable: an exposed remote path, a shared credential, a boundary that existed only on paper. IEC 62443 provides the structure to find and rank those gaps before an attacker does, but only if the assessment behind it is thorough, consistent, and current.
The best IEC 62443 risk assessment platform is the one that reads your evidence, shows its reasoning, keeps your experts in control, and gives leadership a clear, defensible view of risk across every site. Choose it with the same care you would apply to any system that protects people, production, and public trust.
Book a Free Consultation with Our Experts
If you are planning an IEC 62443 assessment, scaling one across multiple plants, or simply want an honest view of where your assessment process stands today, our industrial security specialists are happy to talk it through. There is no obligation and no sales script. Just a practical conversation about your environment, your priorities, and your options.
Book a Free Consultation with Our Experts. Share a few details about your sites and goals, and a Shieldworkz specialist will walk you through how a repeatable, evidence-based IEC 62443 assessment could work for your organization.
Additional resources
A downloadable report on the Stryker cyber incident here
Removable media scan solution vendor evaluation and selection checklist here
IEC 62443-based OT/ICS risk assessment checklist for the food and beverage manufacturing sector here
Get Weekly
Resources & News
See How Our Industry-Leading OT Security Solutions Address Critical Security Challenges
You may also like

How AI Is Changing IEC 62443 Assessments
Team Shieldworkz

Deep investigative threat intelligence report: Alleged SafePay cyberattack on T-Systems
Team Shieldworkz

CEA Compliance Requirements for Power Utilities: What Changes
Team Shieldworkz

OT Media Scan Solution: What to Evaluate Before Securing Removable Media
Team Shieldworkz

G99 cybersecurity evidence pack for UK generators and BESS: What DNOs need to see in the PGMD
Team Shieldworkz

Inside the alleged onsemi Cyberattack: How Far Did Qilin Really Get?
Team Shieldworkz