Prayukth K V
On August 21, 2026, U.S. Coast Guard personnel and FBI agents boarded a foreign-flagged commercial tanker bound for Texas after U.S. authorities identified indications that its onboard network had been compromised by unidentified overseas cyber actors. The Coast Guard confirmed the operation on September 15 following media inquiries. Separately, Iranian media had reported an alleged cyberattack against VL Prosperity near the Strait of Gibraltar on August 7 that reportedly disrupted communications for nearly 30 hours.
Summary
On September 15, 2026, the United States Coast Guard (USCG) confirmed in response to media inquiries that USCG personnel and Federal Bureau of Investigation (FBI) agents boarded the foreign-flagged oil tanker VL Prosperity on August 21, 2026. The vessel, a 333-meter Liberian-flagged Very Large Crude Carrier (VLCC) capable of carrying approximately 2.3 million barrels of crude oil, was intercepted as it moved toward Galveston, Texas. The joint boarding operation was initiated after federal intelligence indicated that the ship's onboard IT/OT network was compromised by overseas cyber actors while transiting the Atlantic Ocean.
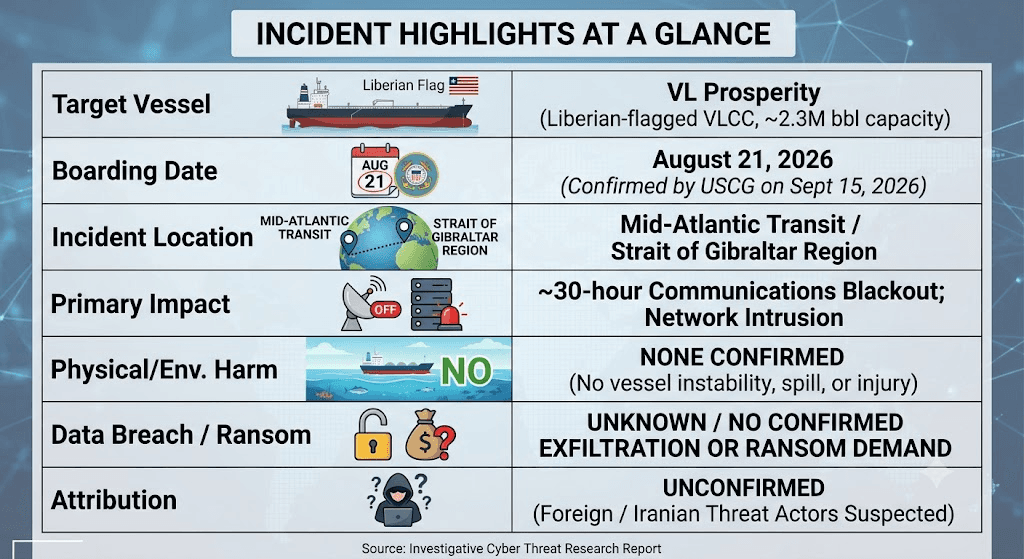
This incident represents a significant escalation in maritime cyber operations, highlighting how remote access compromises on commercial shipping vessels can impact third-parties and directly trigger federal military and law enforcement kinetic interventions to safeguard national critical infrastructure and port security.
What happened? Chronological reconstruction
The following timeline reconstructs the incident from public disclosures by federal authorities, maritime telemetry data, and international news reports.
Date / Time | Event | Source | Evidence Status |
Late August 2026 | Iranian state media (Mehr News Agency) reports that VL Prosperity suffered a 30-hour communications outage near the Strait of Gibraltar due to a cyberattack. | Iranian State Media / Mehr | REPORTED |
Mid-August 2026 | Indications of network compromise by overseas cyber actors detected while the ship transited the Atlantic Ocean towards Texas. | USCG Spokesperson | CONFIRMED |
August 21, 2026 | USCG forces and FBI special agents board VL Prosperity off the coast of Texas to conduct forensic examination and containment. | USCG / FBI Statement | CONFIRMED |
August 22–Sept 14 | Onboard forensic collection, inspection of operational technology (OT) and satellite communication (SatCom) terminals, and crew interviews. | Maritime Security Sources | ASSESSED |
September 15, 2026 | USCG publicly confirms the August 21 interdiction operation following formal inquiries by Bloomberg News. | USCG Statement via Bloomberg | CONFIRMED |
Current Status | Vessel positioned near Galveston, Texas. Crew co-operated fully; no physical instability, spills, or injuries reported. | USCG Statement / AIS Data | CONFIRMED |
How did the attack happen? Vector analysis
Because official forensic reports remain classified under active federal investigation, initial access mechanisms must be categorized systematically according to available technical indicators.
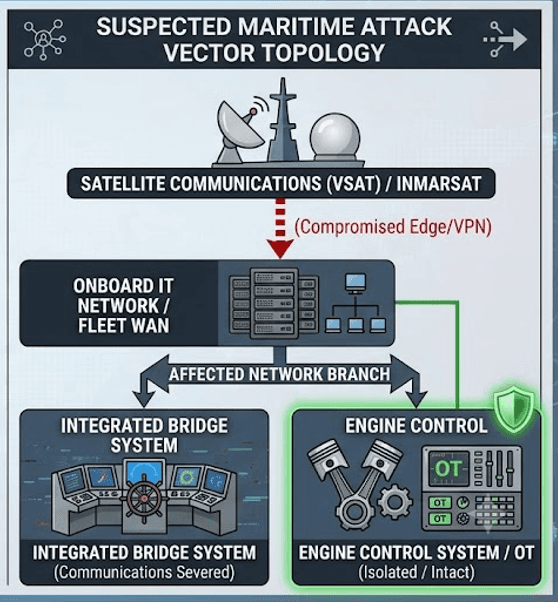
Exposed SatCom / VSAT Gateways:
Evidence found: total loss of vessel communications reported near Gibraltar spanning nearly 30 Hrs.
Assessment: ASSESSED: Highly probable primary vector or secondary target. Exploitation of unpatched shore-to-ship satellite communications, remote management portals, or unencrypted VSAT link management tools frequently leads to network disruption.
Compromised VPN / Remote Maintenance Access:
Evidence found: Ship uses interconnected OT/IT infrastructure for remote monitoring and propulsion controls.
Assessment: ASSESSED: Several attack pathways are technically plausible in maritime environments, including compromised remote-access credentials, exposed management interfaces, supplier/maintenance connections and vulnerabilities in shipboard IT infrastructure. However, no public evidence currently establishes which mechanism was used against VL Prosperity.
Credential Theft / Password Spraying:
Evidence found: No public disclosure of leaked credentials specific to this vessel.
Assessment: UNKNOWN — No reliable public evidence establishes this.
Ransomware / Destructive Wiper:
Evidence Ffound: No operational disruption to vessel stability or propulsion reported; crew operated normally.
Assessment: UNLIKELY / UNKNOWN — No extortion demand, ransom note, or destructive payload has been confirmed.
Systems and services impacted
The investigation revealed key distinctions between compromised communication systems and unaffected propulsion systems.
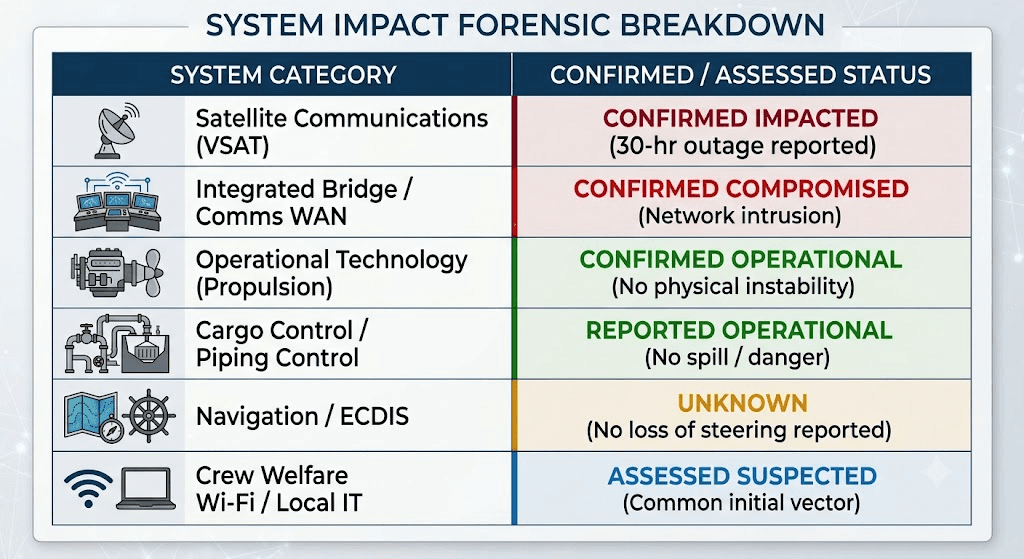
Confirmed Affected Systems: Onboard IT/communications network. Satellite communications were rendered non-operational during transit through the Mediterranean/Gibraltar area.
Confirmed Unaffected Systems: Physical propulsion, ballast control, steering gear, and mechanical oil-handling OT. USCG explicitly verified no loss of vessel control, operational disruption, or environmental hazard occurred.
Unknown Systems: Integrity of the Electronic Chart Display and Information System (ECDIS), Automatic Identification System (AIS) transponders, and onboard maintenance databases.
Data compromise assessment
A central concern in maritime network intrusions is whether threat actors exfiltrated sensitive operational data, navigational telemetry, or crew credentials.
Personal Data & Crew Information: UNKNOWN — Federal authorities have not disclosed whether crew personal identifiable information (PII) or passport details were accessed.
Commercial & Cargo Data: UNKNOWN — No public evidence demonstrates exfiltration of bills of lading, charter party agreements, or cargo manifests.
Exfiltration / Extortion Activity: UNKNOWN — No threat actor has published sample data or listed VL Prosperity on a dark-web leak site.
Operational and recovery impact
Despite the cyber intrusion, physical operational continuity was maintained due to maritime redundancy protocols.
Operational Continuity: The vessel maintained physical transit capabilities across the Atlantic. Standard manual vessel management workarounds were utilized during the communication blackout.
Federal Intervention: USCG and FBI agents boarded the vessel at sea prior to its arrival in Galveston, Texas, isolating affected IT networks to prevent potential cross-contamination with U.S. port infrastructure.
Port Safety: USCG actively managed communications with local port operators and maritime stakeholders to guarantee unhindered energy transport operations.
Threat actor investigation and attribution
Attribution in maritime cyber incidents requires analyzing geostrategic context and regional reporting.
Reporting Origins: Iranian state-aligned outlets (Mehr News Agency) were among the first to publicly detail the 30-hour blackout near the Strait of Gibraltar.
Threat Actor Profile:
Suspected Origin: Overseas Cyber Adversaries / Foreign State-Sponsored Actors.
Attribution Confidence: UNCONFIRMED / MEDIUM ASSESSED.
Geopolitical Alignment: State-backed groups operating out of the Middle East have historically targeted maritime shipping routes (Strait of Hormuz, Bab el-Mandeb, Strait of Gibraltar) for intelligence collection, signal disruption, or asymmetric leverage.
Corroboration: Federal agencies (USCG/FBI) confirmed foreign actor network compromise but refrained from formally naming a specific APT (Advanced Persistent Threat) unit.
Broader sectoral pattern analysis
This incident fits within a documented surge of cyber campaigns targeting energy supply chains and international maritime logistics from 2024 through 2026.
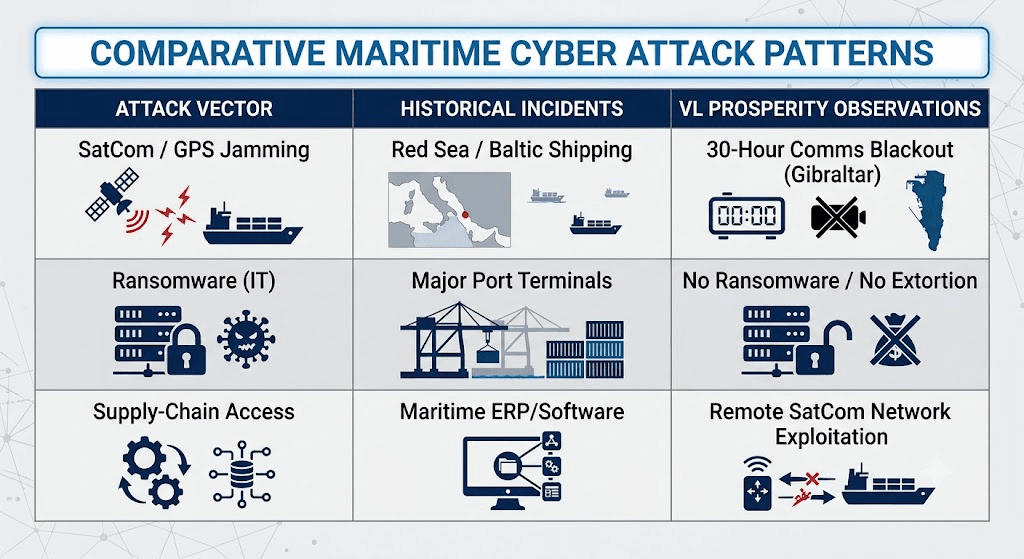
SatCom and Remote Access Exploitation: Commercial vessels increasingly rely on interconnected VSAT and OT networks for remote maintenance, creating an expanded attack surface for adversary reconnaissance.
Energy Logistics Vulnerability: Tankers carrying high-volume crude (~2.3M barrels) represent strategic targets where even minor network anomalies trigger federal law enforcement intervention due to environmental and national security risks.
Structural vulnerabilities in commercial maritime security
Maritime assets face systemic cybersecurity challenges distinct from traditional land-based enterprise environments:
IT/OT Convergence at Sea: Modern tankers integrate engine diagnostics, navigation, and satellite communication over shared local networks without strict air-gapping.
Exposed Satellite Edge Devices: VSAT terminals, satellite routers, and maritime communication hubs are frequently exposed directly to the internet with unpatched firmware or default credentials.
Complex Flag-State Governance: Dual oversight between flag states (e.g., Liberia), operating companies, and international port authorities complicates rapid patch management and incident reporting.
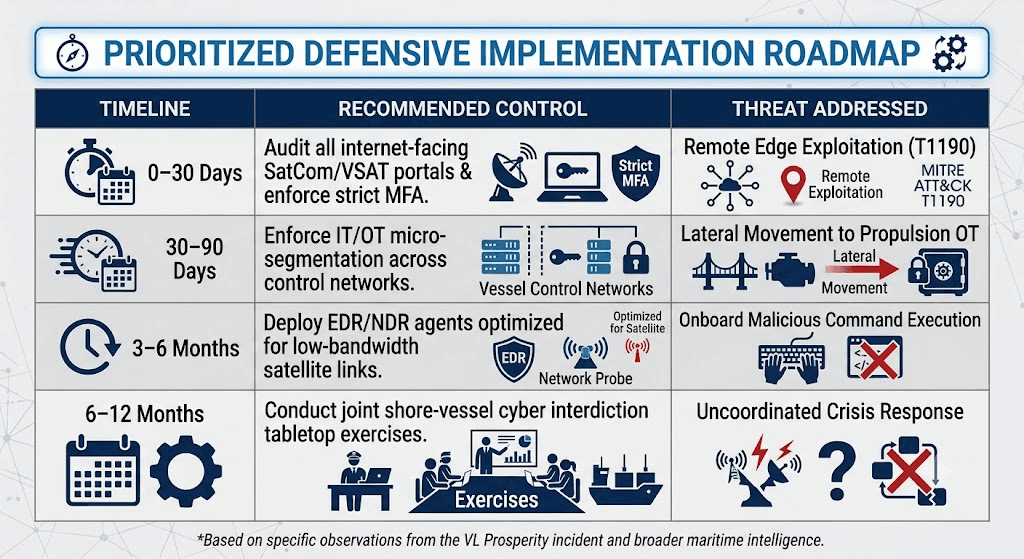
Bandwidth & Patch Constraints: Vessels at sea face severe bandwidth limitations, delaying security updates and EDR telemetry synchronization.
Potential MITRE ATT&CK Mapping
The following mapping reflects evidence-supported techniques observed or assessed in this incident.
Technique | Relevance | Evidence |
T1190 – Exploit Public-Facing Application | Possible if an exposed maritime service was exploited | No public evidence |
T1078 – Valid Accounts | Possible remote-access scenario | No public evidence |
T1021 – Remote Services | Possible maritime remote-management pathway | No public evidence |
T1489 – Service Stop | Could potentially describe communications disruption | Causal mechanism unknown |
T1562 – Impair Defenses | Possible if security controls were deliberately disabled | No public evidence |
These techniques are analytical hypotheses and should not be interpreted as confirmed attacker behaviour.
Defensive lessons and mitigations
To protect commercial vessels and OT infrastructure from similar overseas intrusions, maritime operators must implement layered defenses:
SatCom and Edge Hardening: Enforce strict firewall rules on VSAT management interfaces. Mandate hardware-backed multi-factor authentication (MFA) for all shore-to-ship remote administration portals.
Strict IT/OT Network Segmentation: Implement physical micro-segmentation (IEC 62443 standard) between onboard crew Wi-Fi, navigation bridge networks (ECDIS/AIS), and engine room OT networks.
Immutable Logs and Offline Telemetry: Store network logs on tamper-proof onboard storage to support post-incident forensics even during complete communications blackouts.
Maritime Incident Playbooks: Train vessel officers to execute manual maneuvering and navigation protocols immediately upon detecting network degradation or SatCom failures.
Prioritized action matrix for maritime and OT operators
Key unanswered questions
What was the exact initial access vector used to compromise the vessel's network?
How long did foreign cyber actors maintain undetected access prior to the Gibraltar communications outage?
Were onboard navigation (ECDIS) or propulsion control systems directly targeted, or was the intrusion confined to the communications bridge?
Which specific foreign threat group or nation-state proxy orchestrated the intrusion?
Did the attackers exfiltrate cargo manifest or vessel tracking data before detection?
Shieldworkz assessment
The interdiction of VL Prosperity by the US Coast Guard and FBI represents a significant milestone in maritime cybersecurity enforcement. While public evidence confirms a foreign cyber compromise that disrupted communications for 30 hours, there is currently no evidence indicating physical damage, environmental hazard, or operational control takeover.
The primary threat vector appears to center on vulnerable satellite communications (SatCom) and remote maintenance portals exposed during oceanic transit. The swift boarding operation demonstrates that Western maritime authorities treat cyber anomalies on heavy crude carriers as critical national security threats requiring immediate physical intervention prior to port entry.
The reported communications outage makes maritime communications infrastructure a relevant investigative area, but there is currently insufficient public evidence to determine whether SatCom infrastructure was the initial access vector, an affected system, a secondary target, or unrelated to the underlying compromise.
It must be remembered that this event is not yet a confirmed cyber-physical attack on a tanker. It is a confirmed U.S. federal investigation into indications that a foreign commercial vessel's network had been compromised. The alleged 30-hour communications blackout and alleged manipulation of engine-room systems provide important investigative leads, but remain unverified in publicly available evidence.
Recommended Reading from Shieldworkz
For detailed playbooks and regulatory guidance on securing OT and critical infrastructure assets, refer to the following Shieldworkz resources:
Shieldworkz Regulatory Playbooks: Operational compliance and security frameworks for OT environments.
Sources
U.S. Coast Guard & FBI Statement via Bloomberg News (Reported Sept 15, 2026).
Straits Times / Reuters Reporting: US Coast Guard boards oil tanker in cyberattack investigation(Sept 16, 2026).
Mehr News Agency (Iran): VL Prosperity Vessel Communication Disruption Report (Late August 2026).
Shieldworkz Cyber Intelligence Repository: OT Security & Regulatory Compliance Assets.
Get Weekly
Resources & News
See How Our Industry-Leading OT Security Solutions Address Critical Security Challenges
You may also like

Investigative cyber threat research report: Cyberattacks on U.S.-bound energy tankers
Team Shieldworkz

The OT Lull: What a 30-day decline in direct intrusion activity actually tells us
Prayukth K V

Inside the Revolut data disclosure incident
Prayukth K V

NERC CIP Compliance Software: 9 Capabilities Utilities Should Compare
Team Shieldworkz

Central Electricity Authority Cyber Security Regulations: Complete Guide
Team Shieldworkz

Inside the Kimberly-Clark / ShinyHunters Incident
Team Shieldworkz